16 ACTIVE SENSORS · 10-SECOND LIVE SAMPLING

Active prevention, systems telemetry, and lightweight EDR for Windows

KuraGuard unifies hardware health monitoring (including predictive S.M.A.R.T.), 3 layers of live EDR defense, OS attack surface hardening, and operational continuity into a single native service with ~0% idle CPU across Windows Server 2012 through Windows 11 and Server 2025.

Select your operational view:

INTERNAL IT DEPARTMENTS

Operational calm, compliance hardening, and continuity for your organization

For corporate systems administrators, KuraGuard delivers live 10-second visibility and proactive defense. Predict physical disk failures with S.M.A.R.T., monitor Automatic-start critical services, track expiring SSL certificates, and enforce GDPR / ISO 27001 compliance across BitLocker, Firewall profiles, and Local Administrators.
-65% in reactive internal support tickets
Operational calm, compliance hardening, and continuity for your organization

~0% CPU via Kernel Watchers

Uses native asynchronous Windows kernel listeners instead of heavy scans. Includes a password-protected bilingual (ES/EN) local console with Excel/CSV export.

OS Hardening & Operational Continuity

Monitors Defender, all 3 Firewall profiles, BitLocker, listening TCP ports, RDP sessions, stopped automatic services, pending updates, and SSL certificate expiration.

3 Layers of Live EDR Defense

Zero-delay anti-ransomware Honeypots, PowerShell malicious script hunting (Event ID 4104), and critical alerts on unauthorized Local Administrator elevation.

MSPs & IT SERVICE PROVIDERS

Profitability, strict multitenancy, and self-closing alerts for MSPs

For IT service companies and MSPs, KuraGuard multiplies technician efficiency. Manage dozens of clients under a strict multitenant hierarchy, eliminate false alarms with persistence-based thresholds, and let incidents resolve automatically via Self-Healing Alerts.
3x more endpoints supervised per engineer
Profitability, strict multitenancy, and self-closing alerts for MSPs

Multitenant Hierarchy & Critical Heartbeat

Isolate clients and branch offices cleanly and flag critical servers, domain controllers, or POS systems for instant offline alerts.

Self-Healing Alerts & Persistence

Alerts only trigger when CPU/RAM saturation persists for several minutes, and automatically close in the panel once a service restarts or disk space is freed.

Instant Central Panel Onboarding

Install the agent on the endpoint and it automatically appears in your central panel ready to assign and configure, with subsequent background updates running unattended.

ROBUST ENGINEERING

How KuraGuard Technology Works

A resilient 3-tier distributed architecture engineered around local encryption, kernel events, and minimal resource impact.

01

1. Windows Local Agent (C#)

24/7 Windows Service with asynchronous kernel Watchers and an encrypted local SQLite database. Samples hardware every 10 seconds and intercepts security events in real time.

02

2. Central KuraGuard Cloud

Cloud engine that synchronizes live telemetry, processes automated Self-Healing Alerts, tracks critical server Heartbeats, and calculates fleet health.

03

3. Unified Cloud & Local Console

Centralized multitenant web console complemented by a password-protected local agent console with direct audit export to Excel/CSV.
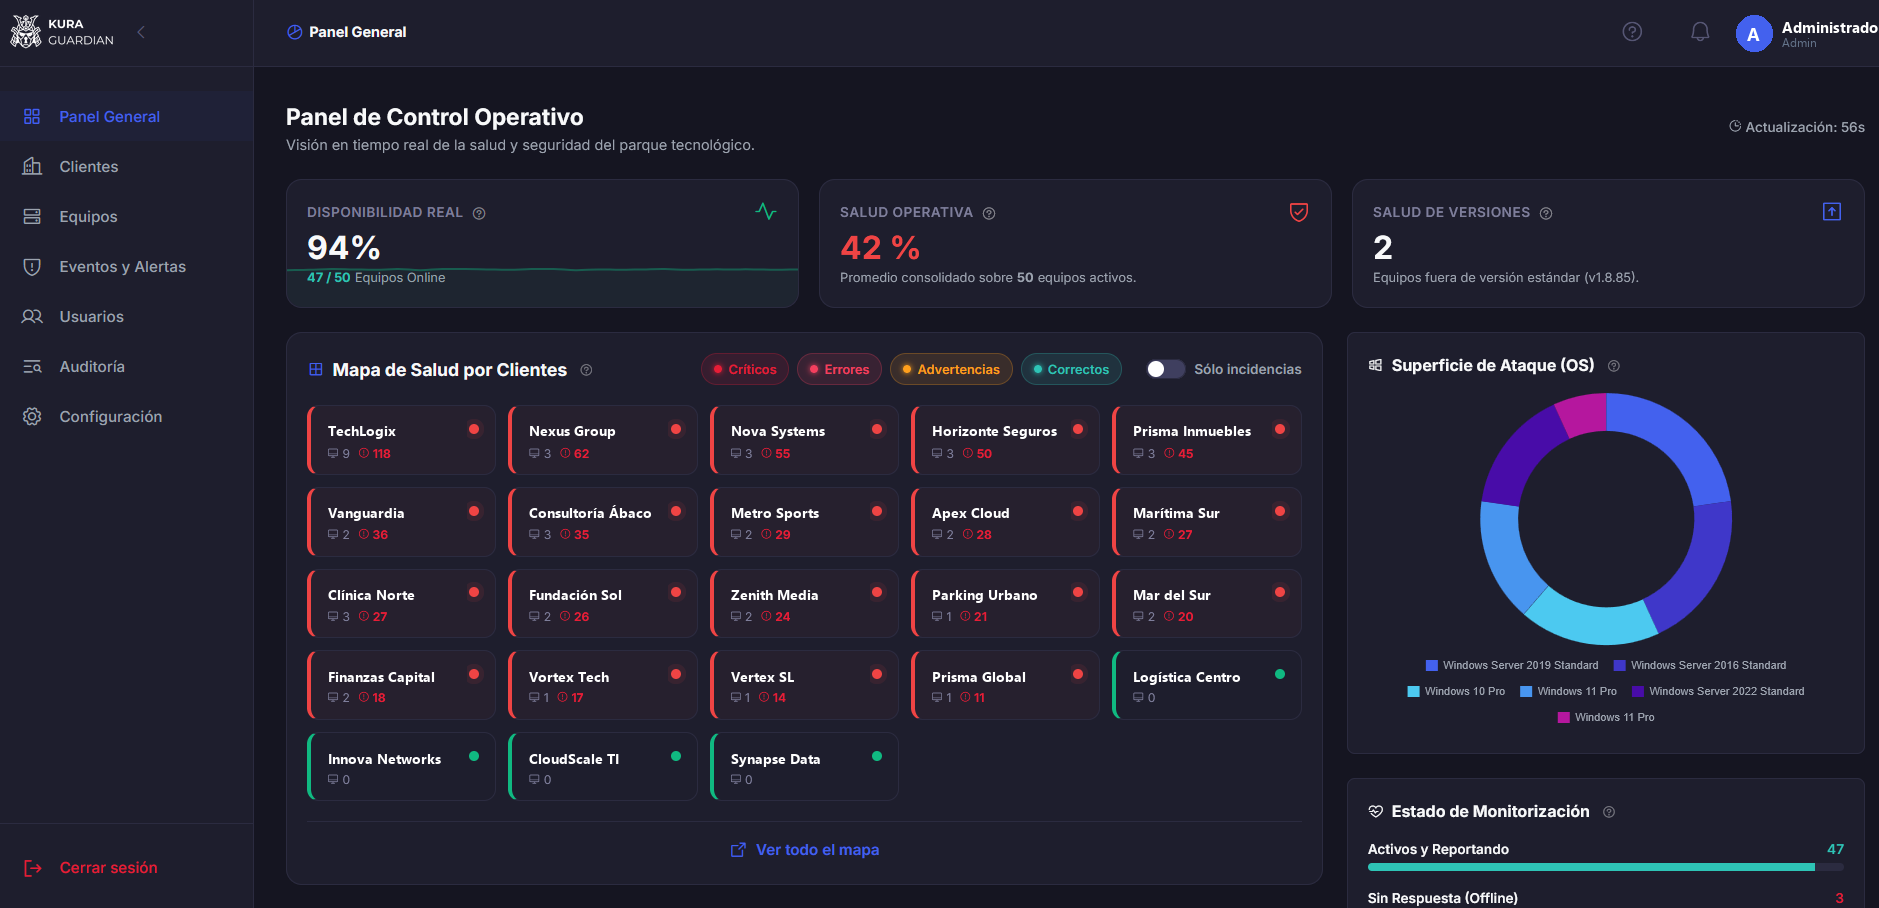
KuraGuard unified cloud management console
THE 4 MONITORING PILLARS

Comprehensive X-ray: all 16 sensors and 22 agent controls

Everything the KuraGuard local agent monitors every 10 seconds and through live Windows kernel listeners.

Pillar A: Real-Time Hardware Performance & Health (10s Cycles)

  • Processor Load (CPU): Real-time average load, max/min peaks, historical chart, and smart persistence alerting.
  • Physical Memory (RAM): Used, available, and total memory (MB/GB and %) via triple native redundancy and sustained saturation alerts.
  • Multi-Disk Storage: Automatic detection of local physical drives (C:, D:, E:), ignoring virtual cloud drives, with dual Warning & Critical thresholds.
  • Predictive Disk Health (S.M.A.R.T.): Direct hardware reading to predict imminent physical failures on HDDs or SSDs (OPTIMAL vs DANGER).
  • Network Latency & Connectivity: Continuous measurement in milliseconds (ms) to the default gateway or a configurable critical IP.

Pillar B: Active Cybersecurity & Live EDR Defense

  • Anti-Ransomware Shield (Honeypots): Strategic kernel-monitored decoy files that fire an instant critical alert (0s delay) upon encryption or deletion.
  • PowerShell Malicious Script Hunting (Event ID 4104): Detects Base64 commands (-enc), DownloadString, Invoke-Expression, or Shadow Copy deletion attempts.
  • Privilege Control (Local Administrators): Immediate critical alert if a user is created or elevated to Local Administrator without authorization.
  • Software Install & Uninstall Auditing: Real-time detection of any newly installed or removed program to prevent shadow IT.
  • Hosts File Guard (Anti-Pharming): Live monitoring of \drivers\etc\hosts against malicious DNS redirection.
  • Process Masquerading Detection: Ensures no malicious executable impersonates the KuraGuard security process from temporary or download folders.

Pillar C: OS Hardening & Attack Surface Control

  • Windows Defender Status (Antivirus): Continuously verifies that real-time antivirus protection is active and alerts if disabled.
  • Windows Firewall (3 Profiles): Separately monitors Domain, Private, and Public firewall profiles, flagging any open exposure.
  • BitLocker Disk Encryption: Checks system drive BitLocker protection (essential for GDPR / ISO 27001 compliance) and alerts if deactivated.
  • Open TCP Port Attack Surface Scanner: Lists all LISTENING TCP ports, bound IP addresses, and mapped services (RDP, SMB, SQL, HTTP, RPC).
  • Remote Desktop Sessions (RDP): Detects and counts active remote desktop sessions on the server or workstation in real time.

Pillar D: Operational Continuity & Forensic Auditing

  • Critical Windows Services Watch: Detects stopped Automatic-start services (SQL Server, IIS, ERP) and notifies when they start back up.
  • Windows Update & Pending Reboots: Tracks pending security updates and warns if a pending reboot is blocking patch installation.
  • True Uptime Tracking: Calculates real time without rebooting (discounting misleading Windows sleep/hibernation) and alerts when exceeding day limits.
  • Digital / SSL Certificate Expiration: Scans the machine certificate store and warns in advance (e.g., 30 days prior) before certificates expire.
  • Critical Inactivity Monitor (Heartbeat): Flag key servers, POS terminals, or domain controllers as critical for immediate offline alerting.
  • Centralized Windows Event Log Collection: Live filtering of critical events: brute-force logins (4625), audit log wipes (1102), service crashes (7034), BSODs (41), and disk errors (7).
ENGINEERING DATASHEET

Built from the ground up for peak efficiency on Windows

Every component of the local agent and cloud platform is engineered for 24/7 unattended operation without taxing your systems.

Agent Architecture
Async Kernel Watchers (~0% CPU)

Uses native Windows kernel event listeners instead of heavy polling scans, maintaining ~0% CPU consumption at idle.

Local Database & Console
Encrypted SQLite + Bilingual Console (ES/EN)

Encrypted local storage with real-time cloud synchronization, password-protected local console, and Excel/CSV audit export.

Sensors & Sampling
16 Active Sensors · 10s Cycles

Live 10-second sampling with spike smoothing, historical charts, and direct hardware S.M.A.R.T. predictive health reading.

Alert Intelligence
Self-Healing Alerts + Persistence

Prevents false alarms by requiring sustained CPU/RAM saturation and automatically resolves alerts when the issue is fixed.

Self-Protection & EDR
3 EDR Layers + Anti-Masquerading

Honeypot decoys (0s delay), PowerShell 4104 interception, Local Administrator auditing, and process impersonation defense.

Full OS Compatibility
Windows 10/11 & Server 2012 to 2025

24/7 unattended operation as a Windows Service from Windows Server 2012 through Windows 10, Windows 11, and Windows Server 2022/2025.

Experience the Perfect Balance of Featherlight Speed and Total Control

Install the agent on your Windows workstations and servers, see them immediately in your central console, and automate 24/7 protection.

View Plans & Pricing Try for Free

We use technical and analytics cookies to ensure the console and forms function smoothly under strict European privacy standards. Cookies Policy