ACTIVE PREVENTION, SYSTEMS TELEMETRY & EDR

Take complete control of your entire IT infrastructure or clients from a single cloud console

A lightweight Active Prevention, Systems Telemetry, and EDR agent for Windows workstations and servers. Uses native Windows kernel listeners (asynchronous Watchers) with ~0% idle CPU, live 10-second sampling cycles, and automated incident resolution (Self-Healing Alerts).
~0% CPU At idle (Kernel Watchers)
16 Sensors Hardware, OS & Active EDR
10 sec Live sampling frequency
Self-Healing Auto-closing smart alerts
Fleet Health & S.M.A.R.T. 98 / 100 · Drives OPTIMAL
16 Active Sensors (10 s) ~0% CPU · Async Watchers
3 EDR Layers + OS Shield Honeypots, PowerShell & Admins OK
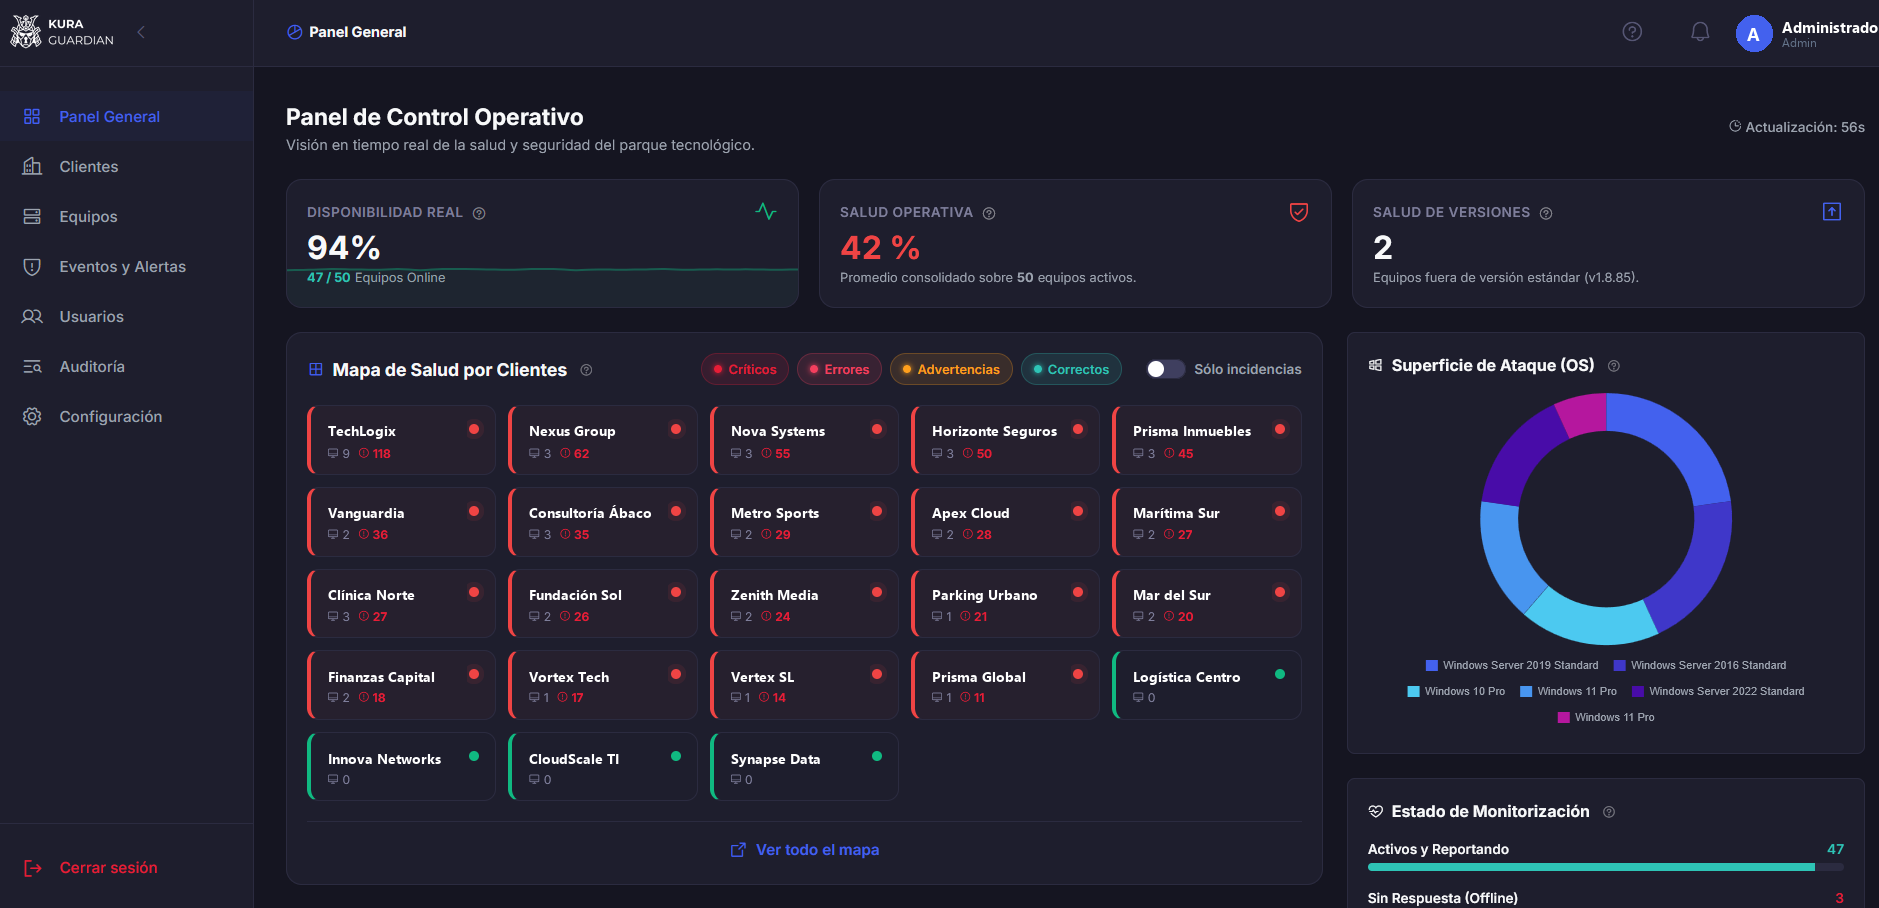
KuraGuard unified cloud management console
Verified native compatibility: Windows 10 & Windows 11 Windows Server 2012–2025 3 EDR Layers & S.M.A.R.T. Self-Healing Alerts Encrypted Local Database
Explore platform

16 active hardware, operating system, and cybersecurity sensors in real time

10s Telemetry & S.M.A.R.T. Health
3 Layers of Active EDR Defense
Automated Self-Healing Alerts
Services, Event Logs & SSL Certificates
INSTANT ONBOARDING

From zero to complete fleet visibility in 3 steps

No complex setups or forced reboots: install the agent on each workstation or server and manage everything from the central panel.

01

Install the agent & see it in your panel

Run the lightweight KuraGuard installer on the Windows machine. Within seconds, the endpoint registers and automatically appears in your central cloud panel ready to be assigned and configured.

Instant registration in central console
02

16 active sensors & 10-second sampling

The agent samples CPU, RAM, physical disks, S.M.A.R.T. health, and latency every 10 seconds, while its kernel Watchers guard anti-ransomware Honeypots, PowerShell 4104, Local Admins, services, and events.

Real-time synchronization
03

Persistence alerts & Self-Healing closure

Avoid false alarms from brief CPU spikes and enjoy Self-Healing Alerts: when an issue is resolved (disk space freed, stopped service restarted, or BitLocker enabled), the alert closes itself.

Automated Self-Healing resolution
Features

Everything you need to protect and maintain your Windows fleet

Ditch disconnected legacy tools. KuraGuard consolidates 16 active sensors across hardware performance, live EDR defense, OS hardening, and operational continuity into one platform.

Hardware & S.M.A.R.T. Health

10-second sampling of CPU (with smart persistence alerts), RAM, multi-disk space (Warning/Critical), network latency in ms, and predictive S.M.A.R.T. drive health (OPTIMAL vs DANGER).

Anti-Ransomware Shield (0 s)

Hidden Honeypot decoy files monitored at the kernel level. If ransomware attempts to encrypt, modify, rename, or delete files, it fires an instant critical alert (0-second delay).

PowerShell Threat Hunting

Intercepts Event ID 4104 in memory in real time: detects hidden Base64 scripts (-enc), silent downloads (DownloadString), Invoke-Expression, or attempts to wipe Shadow Copies.

Admin & Hosts File Guard

Continuously audits the local Administrators group against unauthorized privilege elevation, monitors \drivers\etc\hosts against DNS hijacking, and stops Process Masquerading.

OS Hardening & Attack Surface

Verifies Windows Defender, all 3 Windows Firewall profiles (Domain, Private, Public), BitLocker encryption, active RDP sessions, and every listening TCP port.

Critical Services & Windows Update

Detects stopped Automatic-start services (SQL, IIS, ERP) and notifies when they recover. Tracks pending security updates, reboot-blocked patches, and expiring SSL certificates.

Software & Forensic Event Logs

Detects live software installs/uninstalls and captures critical Windows Event Logs: brute-force logins (4625), audit log wipes (1102), service crashes (7034), BSODs (41), and disk errors (7).

Self-Healing Alerts

When an issue is resolved (CPU drops, disk space is freed, a stopped service restarts, or BitLocker is enabled), the agent automatically resolves and closes the alert in the panel.

OPERATIONAL SCENARIOS

Engineered for the reality of modern IT operations

Whether you manage internal corporate infrastructure or support dozens of client organizations.
Complete visibility across workstations, laptops & compliance INTERNAL IT DEPARTMENTS

Complete visibility across workstations, laptops & compliance

Predict physical drive failures with S.M.A.R.T., spot machines exceeding uptime day limits, track reboot-blocked Windows updates, and verify that BitLocker, Defender, and all 3 Firewall profiles stay active.
-65% in reactive internal support tickets
24/7 monitoring from Windows Server 2012 through 2025 SERVERS & CRITICAL INFRASTRUCTURE

24/7 monitoring from Windows Server 2012 through 2025

Flag domain controllers, SQL/ERP servers, or POS terminals with Critical Inactivity Heartbeat monitoring. Track stopped Automatic-start services, active RDP sessions, listening TCP ports, and SSL certificate expiry.
99.9% continuity on critical services
Multiply managed endpoints without alert fatigue MSPs & IT SERVICE PROVIDERS

Multiply managed endpoints without alert fatigue

Group your clients in a pure multitenant hierarchy. Receive only genuine persistence-verified alerts and let automated Self-Healing Alerts clean up the dashboard as incidents recover.

3x more endpoints supervised per engineer
~0% IMPACT LOCAL AGENT

24/7 active prevention and telemetry without slowing down your endpoints

The KuraGuard local agent runs as an unattended Windows Service using native kernel listeners (asynchronous Watchers) rather than heavy polling scans. It maintains ~0% idle CPU usage and includes a password-protected bilingual (ES/EN) local console.
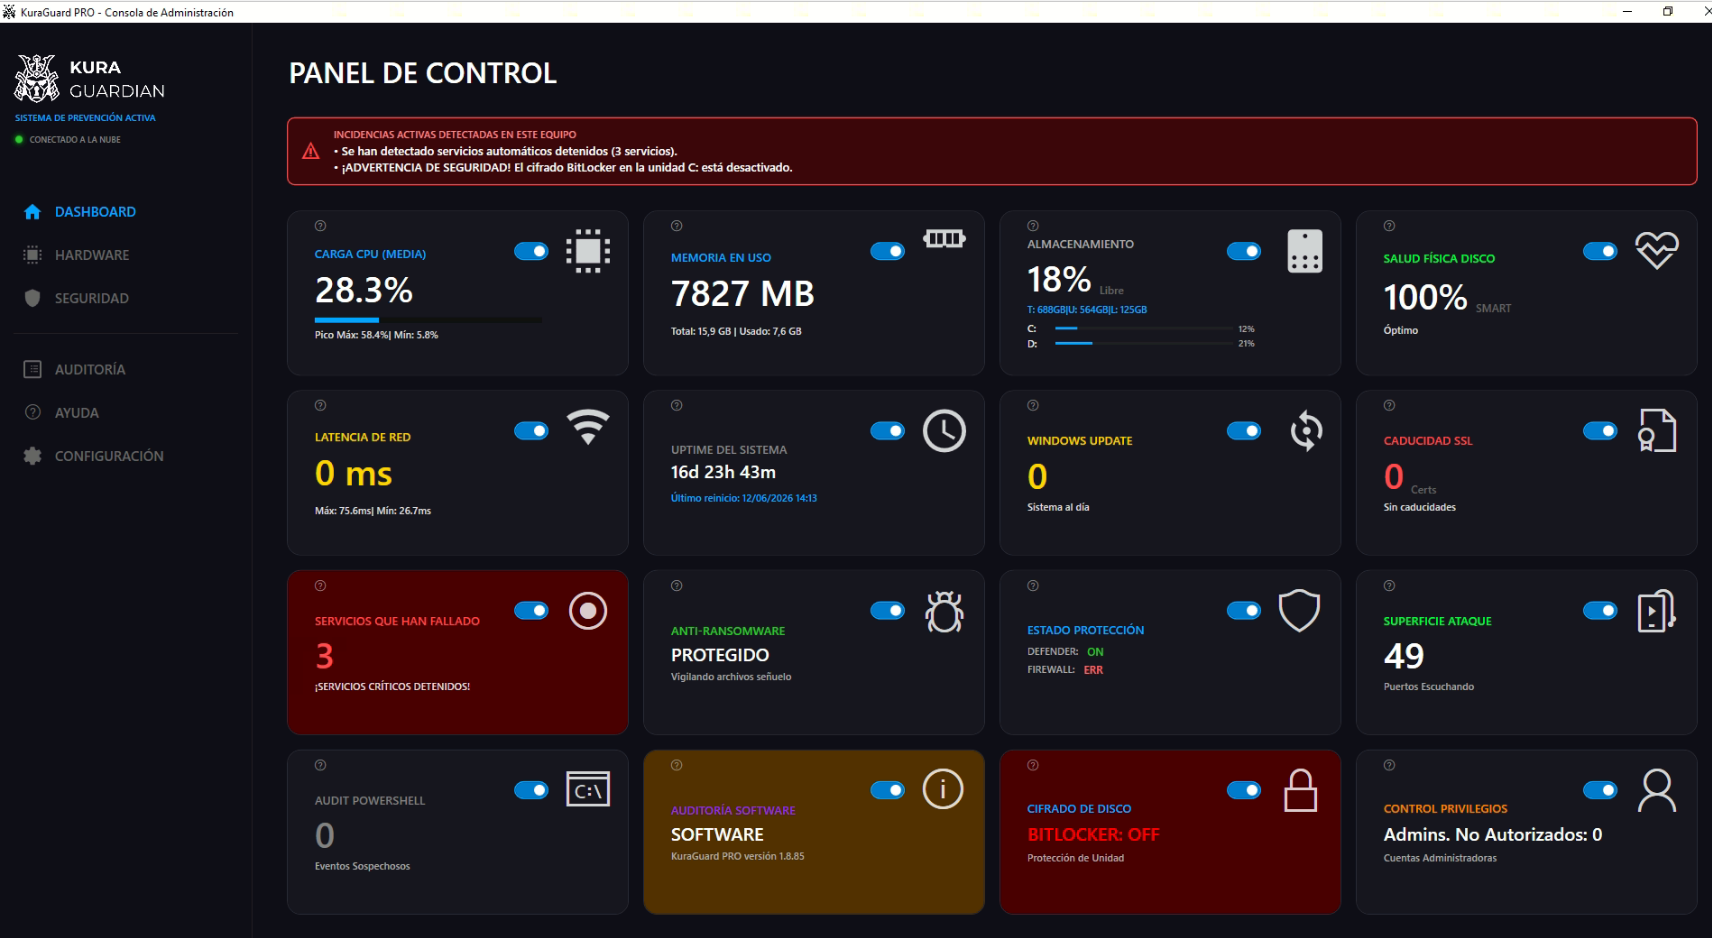
  • Ultra-low footprint (~0% idle CPU) powered by native asynchronous Windows kernel Watchers.
  • Encrypted Local Database (SQLite): Real-time cloud sync plus local audit export to Excel/CSV.
  • Active Self-Protection: Detects Process Masquerading attempts trying to impersonate KuraGuard from temp or download folders.
KuraGuard lightweight Windows agent console
MULTITENANT CLOUD CONSOLE

Control multiple organizations, critical servers, and branch offices in one panel

Engineered for internal corporate IT teams and Managed Service Providers (MSPs). Track fleet health, flag key servers or POS terminals with Critical Inactivity Heartbeat monitoring, and manage noise-free alerts.
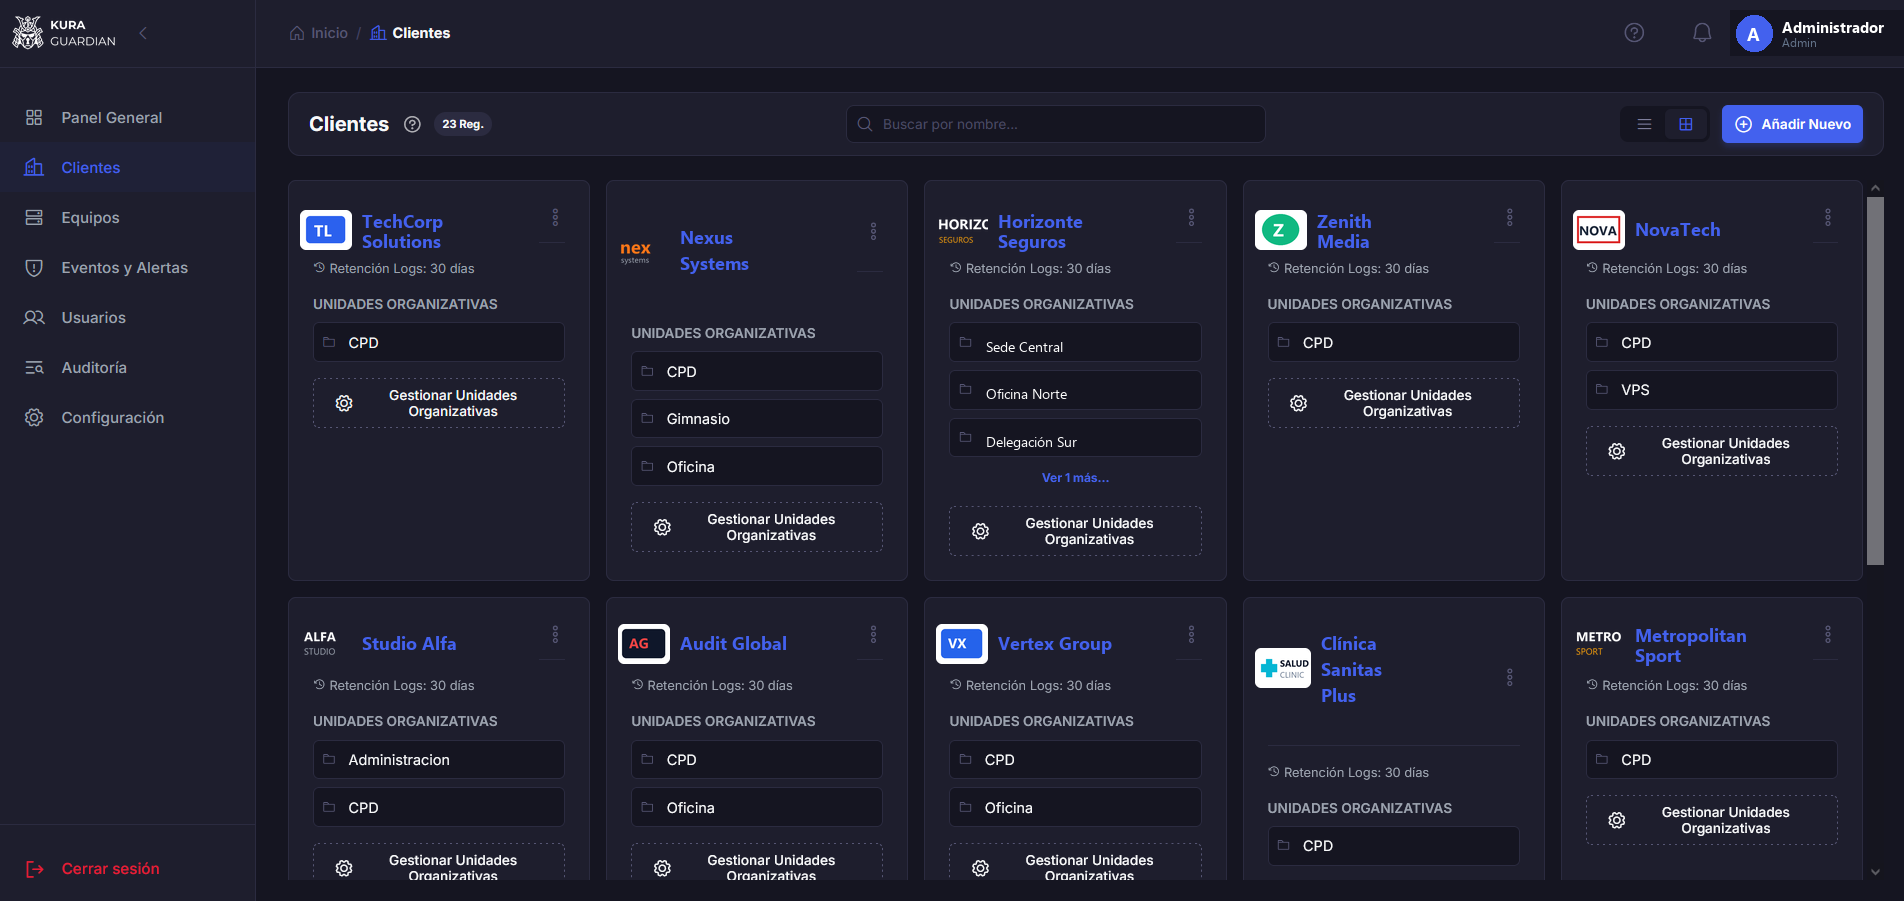
  • Automated Self-Healing Alerts: Incidents automatically resolve in the panel as soon as the metric or service returns to normal.
  • Smart Persistence Thresholds: Only alerts when CPU or RAM saturation persists over several minutes, eliminating false alarms from brief spikes.
  • Critical Inactivity Monitor (Heartbeat): Immediate alert if a key server, domain controller, or POS terminal stops reporting.
KuraGuard multitenant control dashboard
PARADIGM SHIFT

Stop firefighting: move from reactive IT to proactive control

See how daily operations transform for an IT department or MSP when deploying KuraGuard.

Traditional Reactive IT Management

Without unified monitoring or weighed down by bloated tools

  • Finding out a drive failed physically or a critical service (SQL, IIS, ERP) stopped only when an angry client calls.
  • Constant false alarms from momentary CPU spikes and stale alerts that technicians must manually close one by one.
  • Polling-heavy legacy agents that slow down workstations and continuously drain processor cycles.
  • Blindness to ransomware encryption, hidden PowerShell scripts, unauthorized Local Admin creation, or hosts file tampering.
  • SSL certificates expiring unexpectedly, security patches blocked by pending reboots, and sleep modes skewing true uptime.

Proactive Monitoring with KuraGuard

Active prevention, 16 live sensors, and ~0% idle CPU

  • Predictive physical disk health (S.M.A.R.T. OPTIMAL vs DANGER), dual Warning/Critical thresholds per drive, and automatic service monitoring.
  • Smart persistence-based alerting and automated Self-Healing Alerts that close themselves once resources or services recover.
  • Native Windows kernel listeners (asynchronous Watchers) with ~0% idle CPU and live 10-second telemetry cycles.
  • 3 EDR layers (0-second Honeypots, PowerShell Event ID 4104, and Local Admin auditing) + hosts file and Process Masquerading defense.
  • Advance SSL certificate expiry warnings, true Uptime (discounting sleep/hibernation), Windows Update tracking, and forensic Event Log collection.

Get in Touch with Us

Fill out the form below for any technical or business inquiry and we will get back to you within 24 hours.

Cifrado completo de datos de contacto (Zero-Trust)
Respuesta garantizada en menos de 24 horas
Soporte e ingenieros 100% cualificados
Captcha Image

We use technical and analytics cookies to ensure the console and forms function smoothly under strict European privacy standards. Cookies Policy